How an AI Toy Actually Works: App, Firmware, Hardware and Cloud?

Ask a buyer what an AI toy is made of and most will describe a shell, a speaker and a battery. That stops one layer short of the truth. A talking plush or a card-reading story machine is really a small distributed system, and its behaviour is decided long before a child presses anything: by firmware running inside the device, an app only the parent sees, a cloud service that may sit in another country, and a hardware platform that has to keep working when none of the rest is available. When one of those layers is vague in the quotation, the surprises land months later.
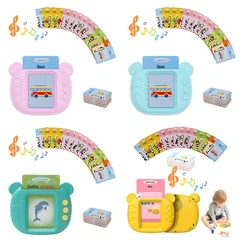
This article maps that system as it is actually built, using the architecture behind XDT's connected audio toys as the reference. It walks through five layers - child, control app, cloud, firmware and hardware - then follows the three signal paths that matter daily: the offline card-tap loop, the remote-request path, and the update channel. It closes with the questions a buyer should ask before tooling, because each is cheaper to answer now than after the mould is cut.
Key Takeaways
- An AI toy is a five-layer system: user, control app, cloud, firmware, hardware.
- The child's experience and the parent's app are deliberately separated; the child never needs a phone.
- Card-tap playback is a local loop, so it keeps working with no network at all.
- Remote requests and updates genuinely need the cloud - and that is where recurring cost and responsibility sit.
- Design around one honest question: what does the product still do when the network is gone?
- Endpoint, data path, certification scope and ownership belong in the contract, not a slide deck.

Two users, one product: the child and the parent
Feature: The system serves two people with opposite needs. A child wants to touch, tap and hear something immediately; a parent wants to browse content, set limits and update the device without handing over a phone.
Advantage: Splitting the interfaces means the child's side is built for durability and zero setup, while the adult's can carry accounts, catalogues and settings a small child should never reach.
Benefit: A toy that a two-year-old can operate alone is a toy that gets used daily, and a toy a parent can quietly configure is one that stays trustworthy in the home.
Evidence: The clearest test is to imagine handing the product to a child with the phone in another room. If it still plays, the separation is right.
Five layers, one system
It helps to think of a connected AI toy as five stacked layers, each with a single job. At the top is the user layer: the child who taps a card or presses a key, and the parent who opens the app to place a request, set a timer or start an update. Below sits the control layer - the app, which pairs the device over Bluetooth, binds it to an account, browses content and sends commands. The cloud layer holds account and device records, distributes audio over a CDN, generates AI stories and text-to-speech where offered, and manages firmware versions. The firmware layer is the device brain: it reads cards, decodes audio, drives the light ring, manages sleep and talks to the cloud. At the bottom is the hardware layer: the module, the NFC reader, the audio codec and speaker, the light ring, the buttons, the battery and the storage.
Two rules keep this stack healthy. First, each layer does only its own job, so a content change never needs new firmware and a firmware fix never needs a new app build. Second, the layers fail independently: a cloud outage should not stop a card from playing, and a disconnected app should never be why a toy goes silent. Most fragile AI toys break one of those rules.
The control layer: what the app does - and what it must not
Feature: The app pairs the device over BLE, browses and queues content, adjusts volume, sets sleep timers and child locks, shows device status, and triggers firmware updates.
Advantage: Keeping these jobs in the app means the toy itself needs no menu, no screen and no keyboard - complexity that would otherwise sit where a child can reach it.
Benefit: The adult gets full control in a place built for adults, while the product a child handles stays simple enough to be safe.
Evidence: App creep is the common failure here. When playback depends on the app being open, the toy can no longer work independently and every household problem becomes a support ticket. Playback should never route through the phone.

The cloud layer: where the toy stops being a toy
The cloud is the layer buyers underestimate most, because it is invisible on the sample table. A typical build holds four things: the account system and device-binding records, the content library and the CDN that delivers audio, the AI story generation and text-to-speech services that give a connected character its voice, and the firmware version manager with its logging and telemetry. The device reaches all of this over MQTT for messaging and HTTPS for downloads, with Wi-Fi or optional cellular.
The moment a product depends on that layer, it inherits an obligation: running costs long after the last unit ships, a security surface, and a support window that has to be decided before tooling. It also raises the questions buyers ask too late - where the endpoint lives, who operates it, what data passes through it, and what happens when the product is retired. The clean way to carry that commitment is to build a product whose core play still works without one.

The firmware layer: the rules the device follows on its own
Feature: A single low-cost module such as the ESP32-S3 runs the device brain on a real-time operating system. It handles Wi-Fi and BLE, MQTT and HTTPS, device discovery and time sync, and the drivers for the audio codec, storage and light ring.
Advantage: Because it runs a proper state machine - card, playing, idle, pairing, updating - the device behaves predictably even when alone, offline and handled by a child.
Benefit: The firmware is where the toy's local business lives: reading a card's identity, looking it up in a table, fetching the matching audio from local storage, decoding it and driving the lights in time with the sound.
Evidence: A capable firmware layer is also the safety layer: volume ceilings, sleep timers, child locks and the offline fallback are enforced here, where no one can override them from a phone.
The hardware layer: the parts you can actually hold
Hardware is the layer a buyer can inspect, and it is where the system gets its physical character. A connected audio toy typically carries a wireless module, an NFC reader tuned to 13.56 MHz for card-tap play, an audio codec and speaker, an addressable light ring, buttons, a battery with charge management, and removable storage. The module fans out over standard buses - I2S for audio, SPI and I2C for peripherals, GPIO for inputs, and a dedicated channel for the light ring - while the enclosure and fabric define how the product feels in a hand and survives a floor.
Two hardware decisions quietly set the ceiling for the whole system. Removable storage decides whether content can grow after launch without touching firmware, and the module choice decides whether the product hits a retail price without cutting parts a child notices. A processor that adds a few dollars rarely improves the experience as much as a better speaker or a smoother card mechanism, so fix the experience first, then find the cheapest hardware that delivers it.
Path A: tap a card and play - the fully offline loop
Feature: A child taps an NFC card on the reader. The firmware reads the card's identity, looks it up in the local table, pulls the matching audio from on-board storage, decodes it and plays it, with the light ring following along.
Advantage: The whole journey happens inside the device. It never touches the app, cloud or network, so it cannot be slowed by a bad connection or broken by an outage.
Benefit: This is the path that suits markets with unreliable connectivity, and the one that keeps working on a plane, in a car or after the brand has moved on.
Evidence: Because the loop is local, its only cost is the card and its content - no server, no subscription, no account. That is why card-tap play is often the most durable feature in a connected product.

Paths B and C: remote requests and over-the-air updates
Two of the three paths run through the cloud, and neither should be able to collapse the product. Follow them to see exactly what the network buys.
Path B - remote request. A parent picks a story in the app. The cloud receives it and pushes a lightweight command to the device over MQTT. The firmware plays the matching audio and reports status back so the app can show what is playing. This is what lets a grandparent send a bedtime story from another city, and it needs both device and cloud to be reachable. If either is missing, the request queues until the device returns - a graceful failure, not a broken toy.
Path C - update. New firmware or audio is uploaded to the cloud and offered to devices, on an app prompt or a periodic version check. A well-built device downloads into a spare partition, verifies the package, and only then switches over, keeping the previous version so a failed update rolls back instead of leaving a brick. With no connectivity at all, the same job is done locally from a card or computer, which costs nothing to operate and never strands a unit.

What the toy still does when the network is gone
Feature: With no connection, card-tap play continues normally, because it is a closed loop between firmware and hardware. Only cloud-dependent features - remote requests and updates - pause.
Advantage: Separating the paths means an outage degrades the product instead of disabling it, so a child never learns that the toy is unreliable.
Benefit: The offline baseline is also the longevity plan. A toy that plays from local content keeps working for years, whether or not the brand still runs a server.
Evidence: The practical test is blunt: switch off the router, hand the toy to a child, and count how much still works. If the answer is "almost nothing," the architecture is upside-down.
What this map means for buyers and brands
Feature: Once the system is drawn as layers and paths, the procurement questions become concrete rather than technical: where the device connects, what data moves, who owns each layer, and what survives an outage.
Advantage: A supplier who answers those questions with a diagram and a contract has built the product before, rather than assembling parts for the first time.
Benefit: Writing the answers into the agreement - endpoints, data retention, certification scope, update method, ownership - removes the two most expensive surprises in connected toys: a server nobody budgeted for, and a firmware black box nobody can maintain.
Evidence: The strongest signal is whether the supplier separates what is theirs from what is yours. Clear boundaries, documented protocols and the option to take firmware and content in-house are what let a brand own an AI toy for years instead of renting it.

Frequently Asked Questions
Does an AI toy need an app to play?
No. Playback is a local loop between firmware and hardware, so a child can tap a card or press a key and hear a result with no phone involved. The app is an adult companion for pairing, browsing, settings and updates - useful, but never a prerequisite for play.
What happens when the Wi-Fi drops?
Local features keep working: card-tap playback, key controls and light feedback all continue, because they never leave the device. Cloud features - remote requests and firmware updates - pause and resume when the connection returns. That split is what keeps an outage from becoming a broken toy.
What does the ESP32-S3 actually do?
It is the device brain. Running a real-time operating system, it manages Wi-Fi and Bluetooth, reads cards, decodes and plays audio, drives the light ring, and handles firmware updates. It also enforces child-safety behaviour such as volume limits and timers - which is why those belong in firmware, not the app.
Where does a child's voice go?
That depends entirely on how the product is specified. An offline card player never uploads anything, because it has no endpoint to send to. A connected conversational toy may stream audio to a cloud service, and then the buyer must know where that endpoint sits, how long data is retained, and how it is deleted. These are contract items, not marketing claims.
How are firmware updates delivered?
Two ways, and the best products support both. Over the air, the device downloads a verified package into a spare partition and switches over only after the check passes, rolling back on failure. Locally, the same firmware loads from a card or computer - free to operate, and able to recover a device with no network at all.
Who owns the cloud and the app?
Whoever the contract says, which is why it has to be written down. In an OEM or ODM build, the brand should know whether the endpoints, accounts and content pipeline are theirs to keep, whether firmware and protocol documentation can be handed over, and what happens if the service is retired. Deciding this before tooling is far cheaper than discovering it after launch.