





AI Toy Privacy by Design: A Practical Guide to Safer Connected Play
An AI toy can feel simple in a child's hands while hiding a complicated data path behind the conversation. A microphone captures speech, software decides when a turn ends, a service may interpret the request, and another service may generate the reply. Privacy therefore depends on the complete system rather than on one feature such as "no camera" or "press to talk."
For product teams, the useful question is what happens from the moment a user activates an AI interactive toy until the response is played, stored or deleted. This guide turns that journey into design decisions that buyers, engineers and reviewers can check before tooling and mass production.
 |
SYSTEM VIEW
Privacy Is an Interaction ArchitectureActivation, capture, processing, storage, user feedback and offline behavior form one experience. A clear architecture reduces ambiguity for families and gives product teams something concrete to test. |
|
01Activate
Show when listening begins and ends |
02Process
Map local and connected services |
03Recover
Define reset, deletion and fallback |
What Does Privacy by Design Mean for an AI Toy?
Privacy by design means making data decisions while the product is being defined. It starts with the function: what must the toy know to answer a question, play a story or remember a preference? The team can then decide which information is necessary, where it is processed, how long it is retained and how the user controls it.
The UK Information Commissioner's Office identifies connected toys as products whose online functions may process personal data. Its guidance emphasizes clear responsibility across the connected-device network, understandable information at purchase and setup, visible indications when collection is active, and avoidance of passive collection. These principles are useful design prompts even though the final legal requirements depend on the product and market.
- Activation: make clear what action starts listening.
- Collection: identify every input, including voice, identifiers and diagnostic data.
- Processing: separate local and remote services in a data-flow map.
- Retention: give stored information a defined purpose and deletion rule.
- Transparency: explain the behavior in understandable product language.
- Fallback: define predictable behavior when a service is unavailable.
Key principle: describe privacy as observable product behavior. A reviewer should be able to activate the toy, disconnect it, reset it and explain what happens at each stage.
The AI Toy Data Path: Questions at Every Stage
| Stage | Question for the Product Team | Evidence to Review |
| Activation | What starts and stops voice capture? | Control description and active-state indicator |
| Capture | Is audio buffered before or after the trigger? | Capture window and firmware events |
| Transfer | What leaves the device and where does it go? | Data-flow diagram and service list |
| Storage | Are audio, transcripts or identifiers retained? | Purpose, access, retention and deletion rules |
| Response | How are safety rules and user feedback applied? | Content policy, fallback lines and test cases |
| Reset | What does a factory reset remove? | Reset procedure and post-reset verification |
Six Design Decisions That Make Privacy Understandable
1. Use a deliberate activation rule
A physical press can create a clear boundary between idle and listening states. If the design uses a wake word or standby listening, specify what is processed during standby and how the active state is shown. The indicator should be understandable without requiring a hidden app screen.
2. Collect only what the function requires
A question-and-answer feature may need a short voice input, but it may not need a persistent profile or long-term storage of raw recordings. Review voice files, transcripts, device identifiers, account details and diagnostic logs separately. Each category should have a purpose rather than inheriting a default retention setting.
3. Separate local controls from connected conversation
Volume, stop, repeat, stored stories and selected routines can sometimes remain local while open conversation uses a connected service. A hybrid architecture may improve continuity and reduce unnecessary network requests. The correct split depends on memory, processing resources, content volume and the intended experience.
4. Design a useful offline fallback
When connectivity fails, silence and repeated error tones make the product feel broken. Define whether the toy plays a short explanation, offers stored content, keeps physical controls available or asks the user to try later. The fallback should be truthful and should not imply that a request was processed when it was not.
5. Make deletion and reset testable
A factory reset, account deletion and content reset may be different operations. Document which information each action removes from the device and remote services. Test the result by reconnecting the toy and confirming that deleted preferences or identifiers do not silently return.
6. Plan for service changes before launch
Connected products depend on software, hosting and third-party services that may change. Decide how security updates, content revisions, service-provider changes and end-of-service communication will be handled. A toy should have a defined useful state even if a connected feature is later reduced or retired.


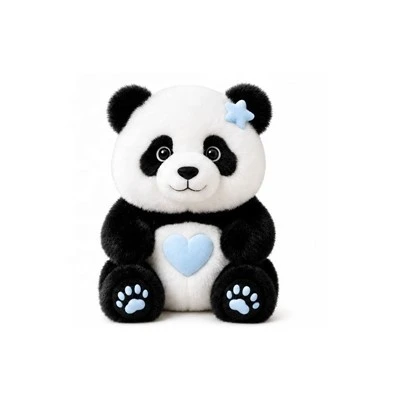
Test activation and feedback inside the complete plush structure. |

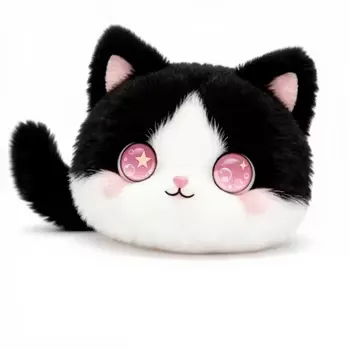
Map visible expressions to clear listening, response and comfort states. |
A Repeatable Privacy and Offline Test Plan
Use one approved firmware build and record the expected behavior before testing. Include normal use and failure conditions:
- Activate and stop listening in quiet and noisy rooms
- Observe every light, sound or movement that indicates collection
- Disconnect the network before, during and after a voice request
- Restart the toy after a failed or interrupted conversation
- Test local buttons, stored content and volume controls without connectivity
- Perform a device reset and any account or cloud deletion process
- Ask a new reviewer to explain the data path using only the packaging and instructions
Record expected result, actual result, firmware version and service environment for each test. Privacy defects often appear as state errors: a microphone remains active longer than expected, an indicator ends too early, a deleted preference returns, or a fallback sends repeated network requests.
Privacy, Safety and Conversation Quality Must Be Tested Together
Data minimization should not make the toy confusing, and a fast response should not bypass safety rules. Product teams need to balance activation clarity, speech recognition, content controls, latency, regional service availability and the user's ability to stop or reset the interaction. A trustworthy toy is one whose behavior remains understandable during normal use, failure and recovery.
Market rules also differ. The FTC's COPPA guidance discusses children's voice recordings and limited situations involving audio used only to fulfill a verbal request. The ICO's Children's Code addresses connected toys likely to be accessed by children in the UK. Product teams should review the final service and data map with qualified legal and compliance specialists for every target market.
From Data Map to a Production-Ready AI Toy
The privacy architecture needs to survive the move from a development board to a finished product. Fabric can hide an indicator, filling can affect microphone pickup, a button can be difficult to locate, and a reset control can become inaccessible. The integrated prototype must therefore be tested with the final plush shell, electronics, firmware, content and packaging instructions.
For teams planning a conversational character, a camera-free AI companion plush toy provides one possible starting direction. Review Xinditai's OEM/ODM development service to align the character, hardware, data path, content and target-market requirements before production.
Frequently Asked Questions
Does a camera-free AI toy automatically protect privacy?
No single feature answers the full question. A camera-free design removes visual capture, but voice, identifiers, service logs and retention still need to be mapped and reviewed.
Is press-to-wake better than continuous listening?
Press-to-wake creates a clear user action and can simplify the interaction boundary. The complete implementation still needs to define capture timing, active-state feedback, processing and retention.
Can an AI toy keep useful functions offline?
Yes, depending on the architecture. Stored stories, playback controls, simple commands or routines may be handled locally while open conversation uses a connected service.
What should a buyer request from a supplier?
Request the feature specification, activation rule, data-flow diagram, service list, offline behavior, reset process, firmware versioning approach and market-specific test plan for the final configuration.
Planning a Connected AI Toy?
Share your audience, target market, activation method, connected functions and offline requirements.